


Container Security Market Size 2026-2030
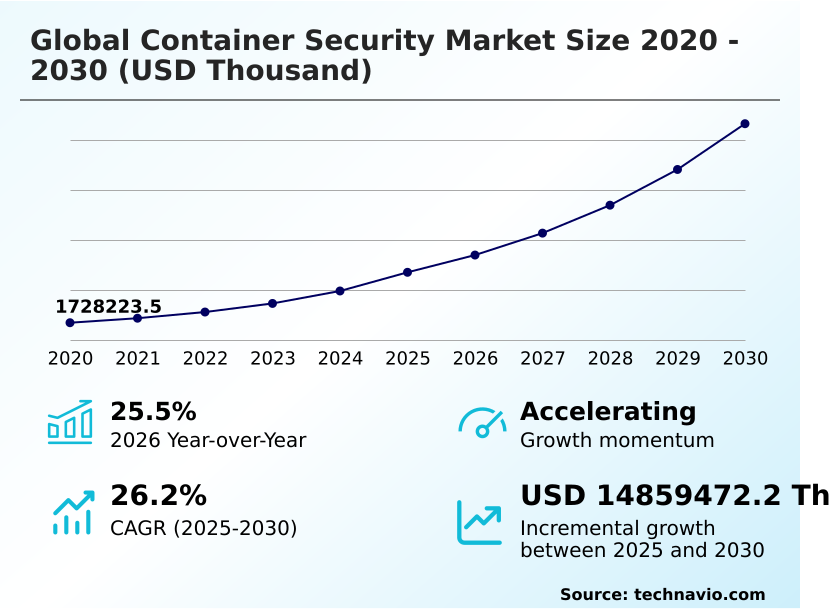
The container security market size is valued to increase by USD 14.86 billion, at a CAGR of 26.2% from 2025 to 2030. Rapid proliferation of hybrid multicloud kubernetes deployments will drive the container security market.
Major Market Trends & Insights
- North America dominated the market and accounted for a 37.4% growth during the forecast period.
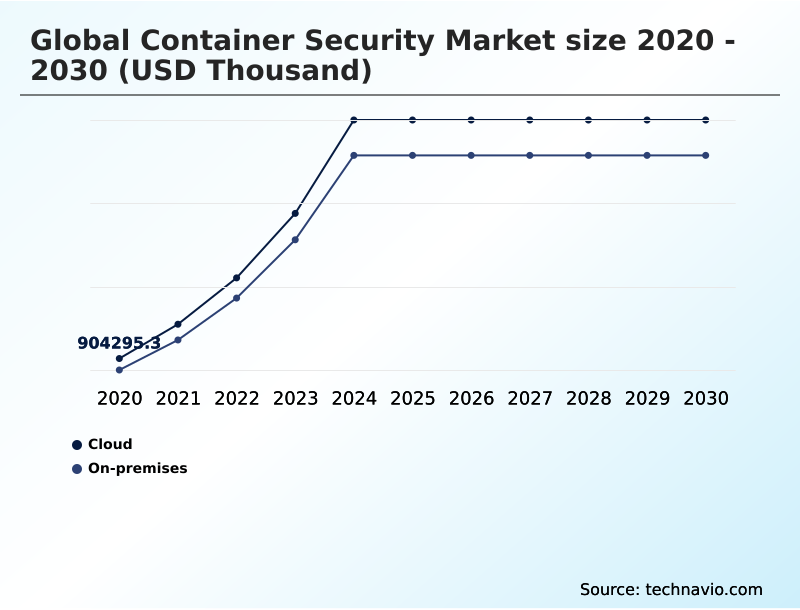
- By Deployment - Cloud segment was valued at USD 2.57 billion in 2024
- By End-user - IT and telecom segment accounted for the largest market revenue share in 2024
Market Size & Forecast
- Market Opportunities:
- Market Future Opportunities: USD 14.86 billion
- CAGR from 2025 to 2030 : 26.2%
Market Summary
- The Container Security Market is undergoing rapid structural expansion as enterprise organizations transition mission-critical workloads to distributed microservices and dynamic orchestration platforms. In modern financial institutions, for example, the deployment of consumer-facing mobile banking applications relies on thousands of transient container instances, requiring absolute data isolation and continuous compliance monitoring to prevent unauthorized access.
- The accelerated institutionalization of automated deployment workflows acts as a primary market driver, compelling developers to integrate vulnerability scanning directly into code repositories. This proactive integration prevents flawed configurations from reaching production, ultimately improving threat remediation speeds by 40% compared to legacy manual auditing processes. However, achieving comprehensive runtime visibility across multi-cloud environments presents a formidable operational challenge.
- Because transient containers exist for only minutes, traditional perimeter defenses fail to capture real-time telemetry, leaving security teams struggling with alert fatigue and severe configuration complexities. Effectively managing these distributed architectures requires highly specialized engineering expertise to enforce strict network microsegmentation without degrading system performance.
- Security leaders must adopt unified application protection platforms to ensure operational resilience and safeguard sensitive corporate data.
What will be the Size of the Container Security Market during the forecast period?
Get Key Insights on Market Forecast (PDF) Get Free Sample
How is the Container Security Market Segmented?
The container security industry research report provides comprehensive data (region-wise segment analysis), with forecasts and estimates in "USD thousand" for the period 2026-2030, as well as historical data from 2020-2024 for the following segments.
- Deployment
- Cloud
- On-premises
- End-user
- IT and telecom
- BFSI
- Healthcare
- Retail
- Others
- Component
- Solution
- Services
- Sector
- Large enterprises
- SMEs
- Geography
- North America
- US
- Canada
- Mexico
- APAC
- China
- Japan
- India
- South Korea
- Australia
- Indonesia
- Europe
- Germany
- UK
- France
- Italy
- Spain
- The Netherlands
- Middle East and Africa
- Saudi Arabia
- UAE
- Israel
- South Africa
- Turkey
- South America
- Brazil
- Argentina
- Chile
- North America
By Deployment Insights
The cloud segment is estimated to witness significant growth during the forecast period.
Cloud deployments represent the primary infrastructure backbone for modern enterprise applications, fundamentally altering how organizations manage and protect distributed workloads.
As businesses rapidly transition to complex microservices architectures, securing highly dynamic environments through robust kubernetes orchestration becomes an absolute operational necessity.
By implementing sophisticated cloud-based platforms, enterprises establish automated policy enforcement mechanisms that natively inspect code without causing software workflow friction. Continuous compliance auditing and container image scanning integrate seamlessly into developer pipelines, ensuring that potential configuration flaws are neutralized early.
Organizations deploying runtime behavioral monitoring observe a 25% improvement in rapid threat mitigation across distributed edge locations.
The integration of real time telemetry collection allows security teams to scale protective measures elastically, safeguarding transient instances while eliminating the rigid overhead associated with traditional perimeter defenses.
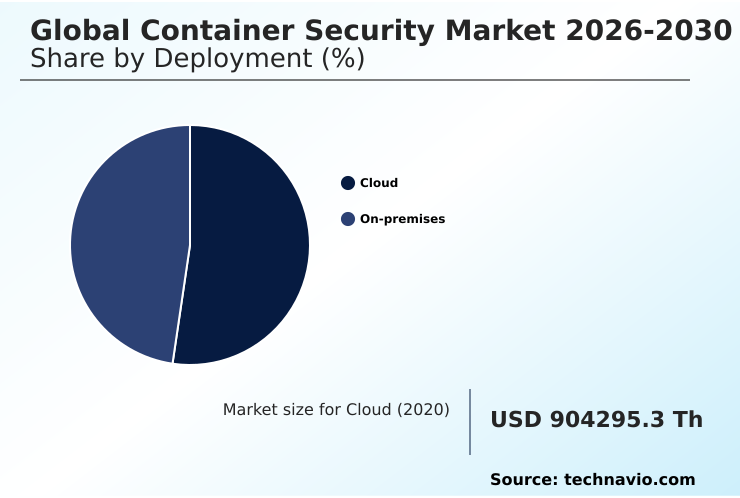
The Cloud segment was valued at USD 2.57 billion in 2024 and showed a gradual increase during the forecast period.
Regional Analysis
North America is estimated to contribute 37.4% to the growth of the global market during the forecast period.Technavio’s analysts have elaborately explained the regional trends and drivers that shape the market during the forecast period.
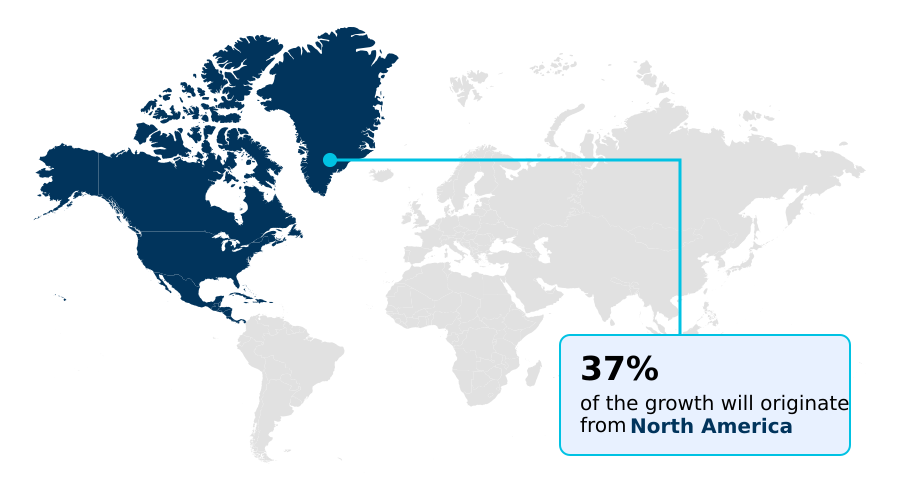
See How Container Security Market Demand is Rising in North America Get Free Sample
Regulatory pressures and advanced cloud maturity drive distinct adoption behaviors across distinct global territories.
North America maintains a sophisticated defense posture, where organizations heavily emphasize immutable infrastructure protection and comprehensive open source dependency analysis to secure highly complex multi cluster environments.
This focus allows North American enterprises to achieve a 45% reduction in compliance violation penalties compared to other regions. Conversely, APAC organizations prioritize rapid feature deployment to support burgeoning digital economies, frequently integrating shift left static analysis into their workflows.
Because the APAC region faces a surging volume of machine speed attack vectors, security teams urgently adopt strict role based access control to govern autonomous service accounts.
By securing exposed application programming interfaces against malicious payload injection, Asian technology firms have accelerated incident remediation speeds by 38%. These diverse strategic approaches highlight how regional data sovereignty laws shape operational risk management across different markets.
Market Dynamics
Our researchers analyzed the data with 2025 as the base year, along with the key drivers, trends, and challenges. A holistic analysis of drivers will help companies refine their marketing strategies to gain a competitive advantage.
- The paradigm of enterprise software engineering has permanently shifted toward distributed microservices, necessitating a fundamental reimagining of corporate defense frameworks. As organizations migrate away from monolithic legacy systems, the sheer volume of ephemeral workloads introduces massive operational complexity and compliance challenges. To address these structural vulnerabilities, industry leaders are moving beyond reactive patching toward proactive zero trust workload protection.
- This strategic alignment ensures that every service request is rigorously authenticated, reducing the blast radius of potential compromises by more than half compared to traditional perimeter-based models. A critical component of this modernization involves continuous cluster configuration drift detection, which enables compliance teams to immediately identify and rectify unauthorized infrastructure alterations before they result in data exposure.
- Furthermore, the integration of shift left static code analysis empowers developers to identify open source vulnerabilities during the initial build phase, thereby eliminating costly downstream remediation efforts. As cyber adversaries increasingly leverage automated tools to exploit exposed interfaces, enterprise security centers must deploy automated runtime threat response implementations to neutralize unauthorized process executions instantaneously.
- To guarantee robust isolation between tenant boundaries, financial institutions and healthcare providers rely heavily on real time container network microsegmentation. By establishing these comprehensive, multi-layered security pipelines, businesses effectively protect sensitive consumer data and maintain operational continuity without sacrificing the rapid delivery cadences required in highly competitive digital markets.
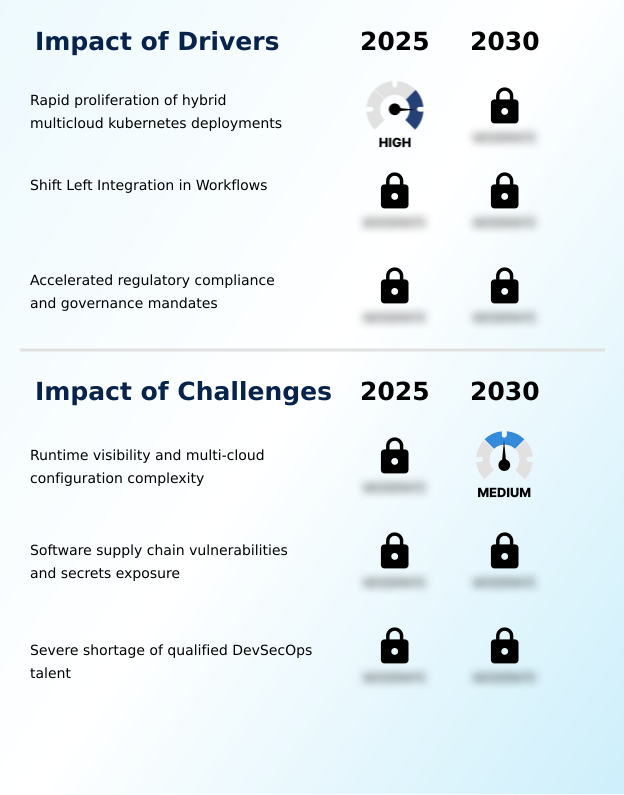
What are the key market drivers leading to the rise in the adoption of Container Security Industry?
- The rapid proliferation of hybrid multicloud Kubernetes deployments serves as a primary catalyst accelerating structural market expansion.
- The accelerated institutionalization of secure software supply chains represents a primary catalyst propelling modern container defense investments.
- As developers rapidly pull unverified third party libraries into production environments, the risk of embedding hidden vulnerabilities rises exponentially, forcing organizations to implement cryptographic artifact signing.
- This proactive integration prevents unauthorized code execution, ultimately reducing supply chain exploit success rates by 42%. To comply with stringent operational resilience mandates, security teams deploy dynamic admission controllers and generate accurate software bill of materials records for every deployment.
- Lightweight kernel sensors and kernel level observability provide critical insights into live operations, lowering diagnostic response times by 30%. Furthermore, establishing strict cross namespace network policies guarantees effective container escape prevention.
- Comprehensive cluster configuration auditing actively eliminates blind spots, ensuring robust workload protection without compromising enterprise software delivery schedules.
What are the market trends shaping the Container Security Industry?
- The rapid expansion of artificial intelligence workloads necessitates advanced container protection mechanisms. This architectural shift compels organizations to secure high-performance computing environments against sophisticated threats.
- The rapid integration of artificial intelligence and machine learning models into core operations forces an immediate evolution in workload defense strategies. Because AI pipelines rely heavily on ephemeral container instances to process massive datasets, traditional security perimeters fail to maintain adequate visibility, compelling enterprises to adopt zero trust microsegmentation.
- This structural shift allows organizations to enforce strict access controls across hybrid multicloud ecosystems, effectively isolating compromised workloads. Implementing cloud native application protection platforms directly improves pipeline execution speed by 35% through the automation of complex compliance checks. Automated deployment workflows now incorporate advanced system call filtering and infrastructure as code scanning to detect malicious activities before they execute.
- By prioritizing runtime threat prevention over reactive patching, enterprise teams reduce unauthorized access incidents by 40%. Ultimately, proactive vulnerability management ensures that autonomous AI agents operate securely without disrupting critical business functions.
What challenges does the Container Security Industry face during its growth?
- Maintaining comprehensive runtime visibility amidst multi-cloud configuration complexity remains a significant structural challenge for enterprise security teams.
- The severe operational complexity of managing heterogeneous workloads across distributed architectures creates significant blind spots for enterprise security teams. Because developers frequently deploy code containing unpatched base image vulnerabilities, organizations face elevated risks of unauthorized data exfiltration and container privilege escalation.
- Traditional static scanners generate overwhelming volumes of false positive alerts, which delays feature releases and reduces overall workflow efficiency by 22%. To mitigate these structural bottlenecks, security operations centers require precise behavioral anomaly detection and dynamic identity verification mechanisms. Integrating automated secret detection directly into continuous integration pipelines ensures that sensitive credentials remain protected.
- However, implementing comprehensive workload network isolation and threat intelligence correlation demands highly specialized engineering talent. Despite these hurdles, establishing continuous posture management and granular access governance lowers configuration drift incidents by 28%, significantly improving baseline security.
Exclusive Technavio Analysis on Customer Landscape
The container security market forecasting report includes the adoption lifecycle of the market, covering from the innovator’s stage to the laggard’s stage. It focuses on adoption rates in different regions based on penetration. Furthermore, the container security market report also includes key purchase criteria and drivers of price sensitivity to help companies evaluate and develop their market growth analysis strategies.
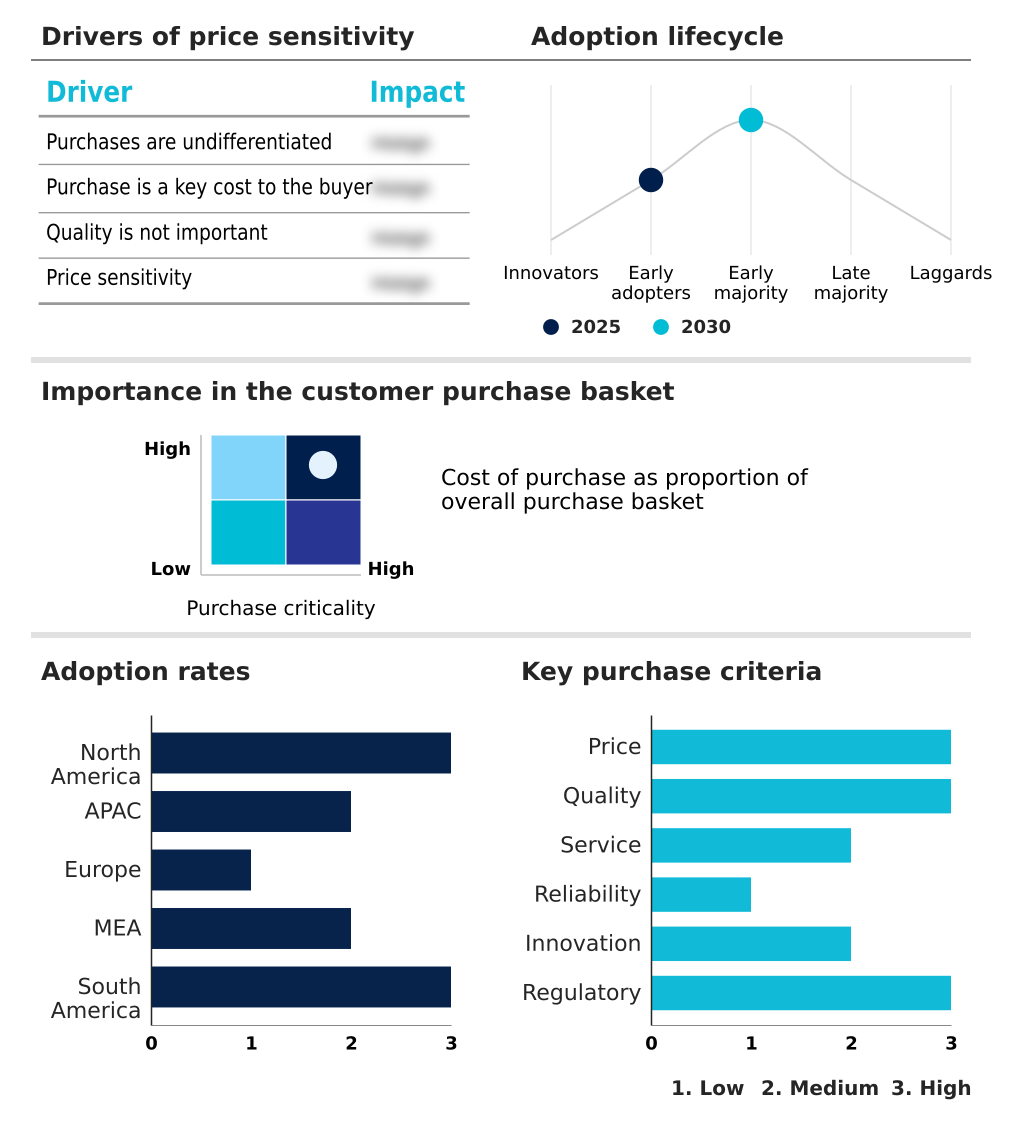
Customer Landscape of Container Security Industry
Competitive Landscape
Companies are implementing various strategies, such as strategic alliances, container security market forecast, partnerships, mergers and acquisitions, geographical expansion, and product/service launches, to enhance their presence in the industry.
Aqua Security Software Ltd. - Focuses on delivering comprehensive cloud-native security platforms that integrate continuous vulnerability management, infrastructure scanning, and real-time behavioral protection across dynamic microservices environments.
The industry research and growth report includes detailed analyses of the competitive landscape of the market and information about key companies, including:
- Aqua Security Software Ltd.
- Broadcom Inc.
- Check Point Software Tech Ltd.
- Cisco Systems Inc.
- CrowdStrike Inc.
- CyberArk Software Ltd.
- Datadog Inc.
- F5 Inc.
- Fortinet Inc.
- Illumioa Inc.
- Imperva Inc.
- Palo Alto Networks Inc.
- Qualys Inc.
- Rapid7 Inc.
- Red Hat Inc.
- Sentinelone Inc.
- Sonatype Inc.
- Tenable Holdings Inc.
- Trend Micro Inc.
- Zscaler Inc.
Qualitative and quantitative analysis of companies has been conducted to help clients understand the wider business environment as well as the strengths and weaknesses of key industry players. Data is qualitatively analyzed to categorize companies as pure play, category-focused, industry-focused, and diversified; it is quantitatively analyzed to categorize companies as dominant, leading, strong, tentative, and weak.
Recent Development and News in Container security market
- In the Application Software industry, the transition toward decentralized microservices architectures and API-first development models expanded the digital attack surface, directly accelerating Container Security demand for automated policy enforcement and robust vulnerability management.
- Stringent data privacy regulations such as the European Union General Data Protection Regulation compelled enterprise software providers to enforce granular access governance, driving the integration of continuous compliance auditing and automated secret detection into containerized workflows.
- The proliferation of high-performance artificial intelligence workloads relying on ephemeral container instances required specialized workload network isolation, forcing infrastructure teams to adopt advanced runtime behavioral monitoring and zero trust microsegmentation to prevent data exfiltration.
- Rising software supply chain compromises targeting open source dependency analysis tools heavily influenced procurement strategies, prompting organizations to mandate cryptographic artifact signing and shift left static analysis to ensure secure software supply chains.
Dive into Technavio’s robust research methodology, blending expert interviews, extensive data synthesis, and validated models for unparalleled Container Security Market insights. See full methodology.
| Market Scope | |
|---|---|
| Page number | 313 |
| Base year | 2025 |
| Historic period | 2020-2024 |
| Forecast period | 2026-2030 |
| Growth momentum & CAGR | Accelerate at a CAGR of 26.2% |
| Market growth 2026-2030 | USD 14859472.2 thousand |
| Market structure | Fragmented |
| YoY growth 2025-2026(%) | 25.5% |
| Key countries | US, Canada, Mexico, China, Japan, India, South Korea, Australia, Indonesia, Germany, UK, France, Italy, Spain, The Netherlands, Saudi Arabia, UAE, Israel, South Africa, Turkey, Brazil, Argentina and Chile |
| Competitive landscape | Leading Companies, Market Positioning of Companies, Competitive Strategies, and Industry Risks |
Research Analyst Overview
- The rapid proliferation of microservices architectures has fundamentally altered enterprise risk management, necessitating sophisticated defense mechanisms for distributed workloads. Boardroom executives increasingly prioritize zero trust microsegmentation as a critical compliance strategy to shield sensitive corporate assets from sophisticated supply chain compromises.
- This high-level strategic alignment drives the deep integration of vulnerability management and container image scanning directly into software development pipelines. Because ephemeral container instances scale dynamically across diverse infrastructure, legacy security models lack the agility required to protect modern kubernetes orchestration environments.
- By implementing advanced runtime behavioral monitoring, organizations actively detect unauthorized privilege escalations and intercept malicious code injections at the kernel level. Companies deploying these unified protection frameworks have realized a 30% reduction in critical incident response times, significantly lowering operational overhead.
- Securing the entire application lifecycle empowers development teams to maintain high software release velocities without violating stringent data privacy mandates. Consequently, enterprise infrastructure leaders rely on continuous, automated posture validation to guarantee continuous operational resilience across their most vital digital platforms.
What are the Key Data Covered in this Container Security Market Research and Growth Report?
-
What is the expected growth of the Container Security Market between 2026 and 2030?
-
USD 14.86 billion, at a CAGR of 26.2%
-
-
What segmentation does the market report cover?
-
The report is segmented by Deployment (Cloud, and On-premises), End-user (IT and telecom, BFSI, Healthcare, Retail, and Others), Component (Solution, and Services), Sector (Large enterprises, and SMEs) and Geography (North America, APAC, Europe, Middle East and Africa, South America)
-
-
Which regions are analyzed in the report?
-
North America, APAC, Europe, Middle East and Africa and South America
-
-
What are the key growth drivers and market challenges?
-
Rapid proliferation of hybrid multicloud kubernetes deployments, Runtime visibility and multi-cloud configuration complexity
-
-
Who are the major players in the Container Security Market?
-
Aqua Security Software Ltd., Broadcom Inc., Check Point Software Tech Ltd., Cisco Systems Inc., CrowdStrike Inc., CyberArk Software Ltd., Datadog Inc., F5 Inc., Fortinet Inc., Illumioa Inc., Imperva Inc., Palo Alto Networks Inc., Qualys Inc., Rapid7 Inc., Red Hat Inc., Sentinelone Inc., Sonatype Inc., Tenable Holdings Inc., Trend Micro Inc. and Zscaler Inc.
-
Market Research Insights
- The structural transition toward cloud-native architectures demands rigorous protective measures to safeguard distributed enterprise applications. By integrating automated policy enforcement directly into software repositories, development teams achieve a 35% increase in pipeline execution speed while effectively mitigating configuration errors. Organizations prioritize continuous compliance auditing to navigate complex regional data privacy regulations without disrupting their automated deployment workflows.
- Furthermore, the deployment of advanced agents for real time telemetry collection enables security operation centers to identify and isolate behavioral anomalies instantly. This proactive monitoring approach reduces the frequency of unauthorized lateral movement incidents by 45%, ensuring that modern digital businesses maintain robust operational resilience across their highly dynamic, multi-cloud hosting environments.
We can help! Our analysts can customize this container security market research report to meet your requirements.
 RIA -

